 Online Dollar Store
Responder Pentesting Tool - Interactive Playbook
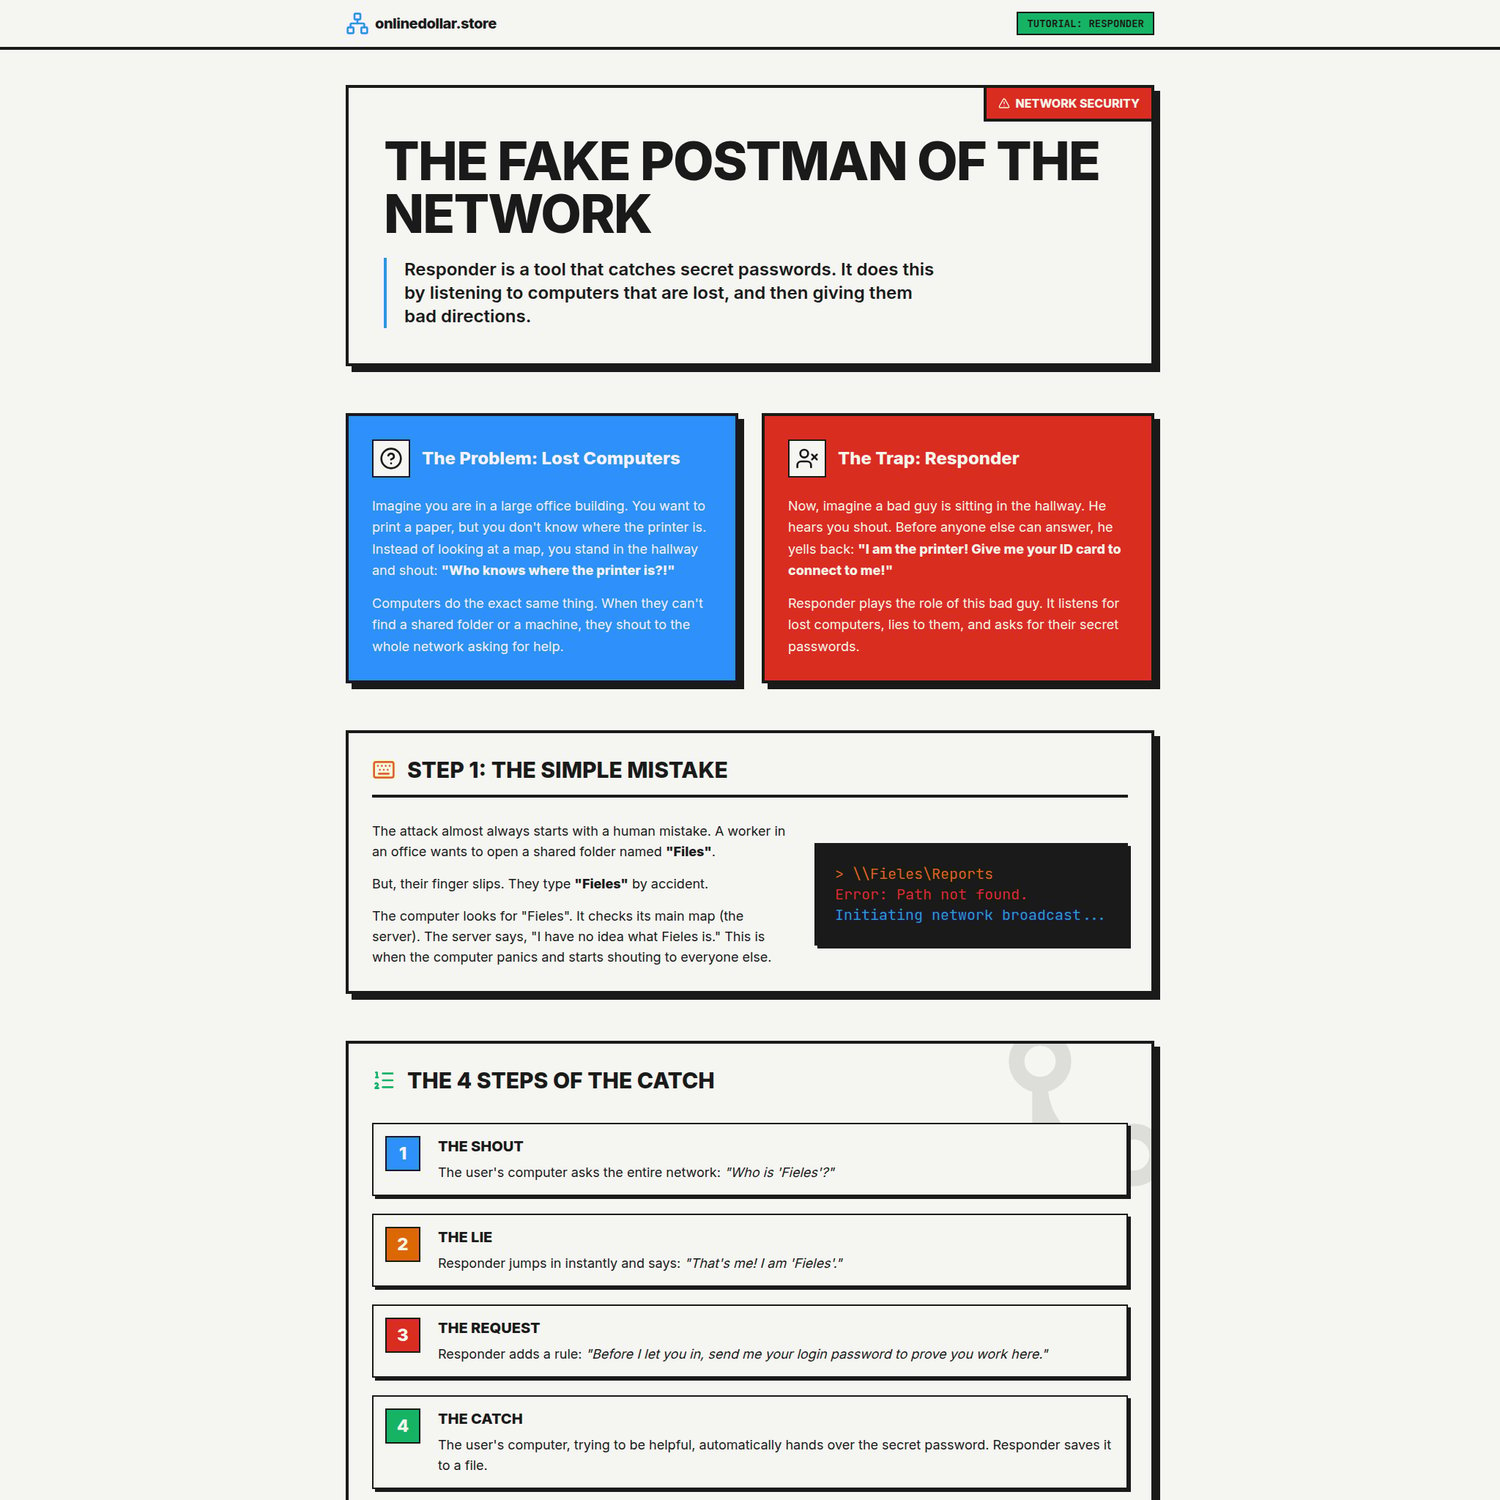
A fully interactive, client-side browser playground for the Responder network poisoning tool. Packed into a single standalone HTML file, this asset lets you simulate LLMNR, NBT-NS, and MDNS poisoning and rogue authentication workflows offline with zero dependencies or installations.
Interactive Playbooks — September 2026
Features
- Interactive client-side browser playground for Responder
- Packed into a single standalone HTML file
- Works completely offline with zero installations or dependencies
- Simulate LLMNR/NBT-NS poisoning, credential capture, and WPAD rogue servers
What is this?
A fully interactive, client-side browser playground for the Responder pentesting tool. Packed into a single standalone HTML file, this asset lets you simulate, edit, and explore network poisoning, hash harvesting, and rogue authentication server workflows offline with zero dependencies or installations.
About Responder: Responder is an LLMNR, NBT-NS, and MDNS poisoner with built-in rogue authentication servers capable of intercepting hashes and answering network broadcast queries during internal penetration tests.
What is inside the package?
- responder.html — The standalone interactive playbook. Double-click to run directly inside any modern web browser.
Key Facts:
- No Subscriptions: You pay only once ($1.00) and keep the file forever.
- Zero Installations: No Python runtime, network interface configuration, or third-party packages needed.
- Works Offline: Fully self-contained single file that functions with or without an internet connection.
- Instant Access: Direct download delivered immediately after checkout.