 Online Dollar Store
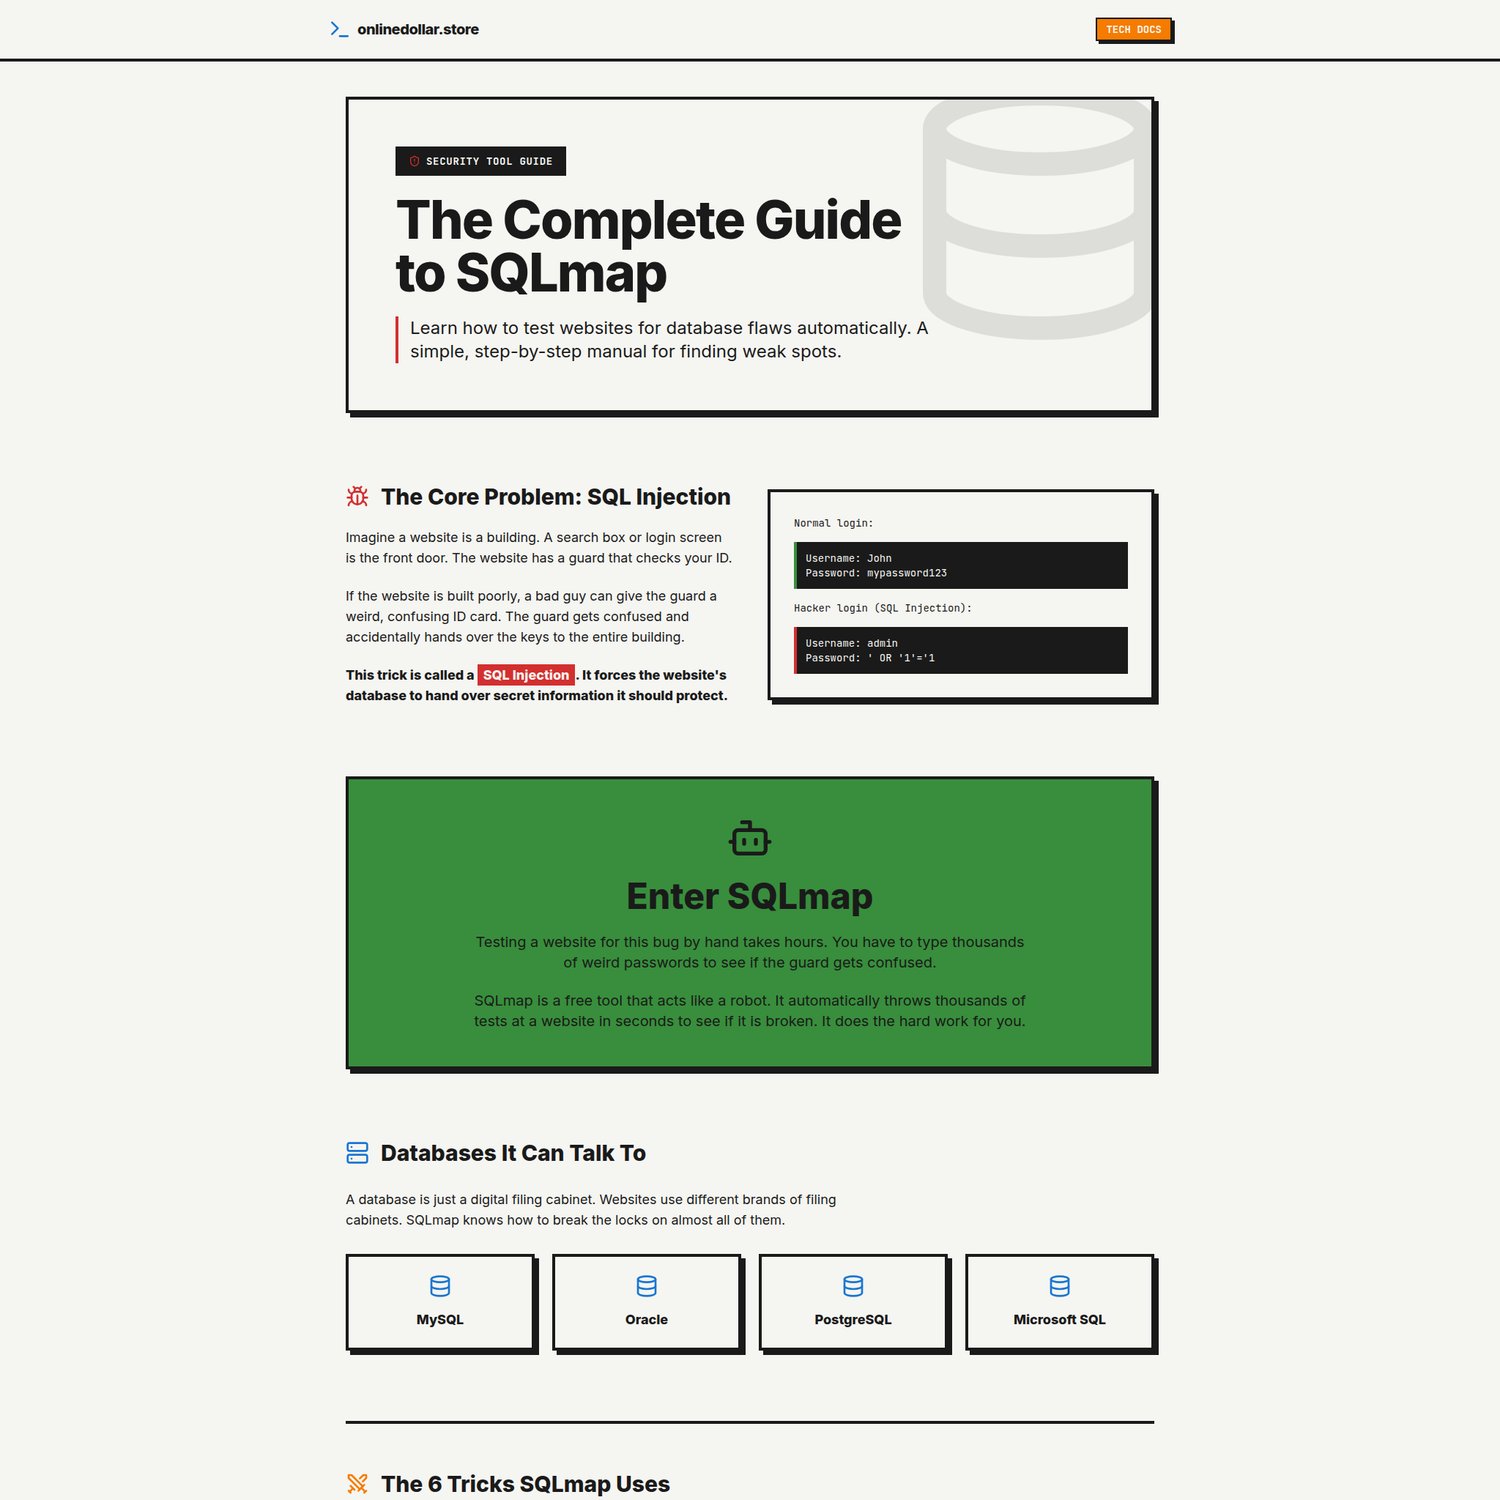
SQL Map Pentesting Tool - Interactive Playbook
A fully interactive, client-side browser playground for the SQLmap database penetration testing tool. Packed into a single standalone HTML file, this asset lets you simulate SQL injection detection, DBMS fingerprinting, and data exfiltration offline with zero dependencies or installations.
Interactive Playbooks — September 2026
Features
- Interactive client-side browser playground for SQLmap
- Packed into a single standalone HTML file
- Works completely offline with zero installations or dependencies
- Simulate SQL injection techniques, tamper scripts, and DBMS extraction
What is this?
A fully interactive, client-side browser playground for the SQLmap pentesting tool. Packed into a single standalone HTML file, this asset lets you simulate, edit, and explore SQL injection detection, enumeration, and exploitation workflows offline with zero dependencies or installations.
About SQLmap: SQLmap is an open-source penetration testing tool that automates the process of detecting and exploiting SQL injection flaws and taking over database servers.
What is inside the package?
- sql-map.html — The standalone interactive playbook. Double-click to run directly inside any modern web browser.
Key Facts:
- No Subscriptions: You pay only once ($1.00) and keep the file forever.
- Zero Installations: No Python environment, database drivers, or third-party packages needed.
- Works Offline: Fully self-contained single file that functions with or without an internet connection.
- Instant Access: Direct download delivered immediately after checkout.